Ansys has been at the forefront in transforming vehicle development using AI-enabled simulation and safety solutions that can reduce time, cost, and complexity across the vehicle lifecycle. In an exclusive interaction with Anwesh Koley of ELE Times, Maitreyee Mordekar, Team Lead, Application Engineering, Ansys (part of Synopsys), delved into the company’s latest automotive innovations and the road ahead for safer mobility.
ELE Times: Please provide a little background about Ansys and what the company is currently involved in.
Maitreyee Mordekar: Ansys, which is a part of Synopsys now, as an organisation, our background is to help customers design systems—not just systems, but go from silicon to systems—to design the entire system-of-systems very effectively. We have different toolchains that enable customers to build, let’s say, their next-gen mobility. When I say mobility, it could be a car, an aeroplane, a railway, or any of those applications.
Synopsys in general has been a market leader in EDA in the semiconductor domain, and Ansys traditionally comes from the simulation and analysis world. When the two things get together, you can actually go from silicon to systems that work together, but are still very, very different. That’s what we enable. That’s just the background that I wanted to give as an organisation, and then we can get into any questions on that front and elaborate.
ELE Times: If you could share your thoughts on safety-critical embedded systems and their criticality in real-time applications.
MM: It’s a very good question to start with. When we think about software in a general audience, we typically think about computer applications, web pages, or mobile applications. But there’s a niche domain which all of us use almost throughout our lifetime—our car, our aeroplane, the railway that we sit on. In these applications, there is software running the car, aeroplane, railway, or industrial applications.
In these situations, there is a very niche factor that plays into the picture: if something goes wrong, it isn’t just the annoyance of a computer not working, but the life of the person inside the vehicle is at stake. That is what safety criticality means.
When we think about safety criticality, it is not just about giving an input and getting an output that is correct; it’s about getting that same output every single time and at the right time. For example, when we are driving a car and someone comes directly in front of it, we press the brake. The brake should work at that exact time, every single time, and at the correct time. That’s what safety criticality means in real-time applications.
ELE Times: If you could share your thoughts on the latest technology trends that you observe in the global and Indian adoption of ADAS technology.
MM: Let me zoom out a little bit and, instead of just focusing on ADAS, look at vehicles as a whole. When cars were built at the start of the automobile industry, it was all mechanical, with hardly any electronics at play. Now, a car is a computer on wheels. Because there are so many situations and tests required, it is difficult to test everything on an actual physical car.
This is where simulation-led development and validating things virtually—what we call virtual validation—comes into play. There is a terminology called a “shift left” in mobility system development, which means testing as early as possible in your developmental cycle.
If you build a system and generate code that is eventually deployed on physical hardware, finding a bug there requires an entire cycle to come back and fix it. However, if you validate things virtually, instead of deploying on a physical ECU, you deploy on a virtual ECU running on your PC. You can observe behaviour directly on your PC, which reduces development time significantly.
This is where the silicon-to-systems perspective helps. You have your software running on your PC alongside physics-based simulations, allowing you to get your vehicle working in a system environment before manufacturing your first physical prototype. Synopsys plays a vital role here by enabling virtual prototyping with our simulation technology.
ELE Times: If you could kindly elaborate on how simulation technology is applied at Ansys and how you see that technology evolving and progressing.
MM: Let’s look at it from the start of building a mobility system like a car or aircraft. Before we start, we have to build the blueprint of the system and determine the components that will go into the vehicle. That can be done using the Ansys System Architecture Modeler, a SysML v2-based tool that helps build a strong perspective of system architecture.
Once you build the architecture, you decompose it into system safety analysis to figure out potential malfunctions, necessary redundancies, additional software models, or required sensors. A tool called Ansys Medini helps perform both functional safety and cybersecurity analysis.
From there, teams work in parallel: some focus on software while others work on the mechanical and physical side of the system. For physics, we have LS-DYNA for crash testing, HFSS for high-frequency calculations, and SPEOS for headlight design and lighting simulation. These are entirely physics-based and as close to reality as possible.
On the software side, because these are safety-critical applications, you use toolchains where you can drag and drop blocks, connect them, and generate code for direct use in the vehicle. For virtualisation, we have tools like Silver and DPT. Across the entire V-cycle for system development, we provide multiple toolchains to equip our customers to build safe vehicles.
ELE Times: How is Ansys translating AI into practical mobility solutions?
MM: As an organisation combining Synopsys and Ansys, we go from silicon to systems. Ansys specialises in simulation, analysis, and physics-based simulation capabilities. We view AI not as a standalone technology, but as something that works closely together with powerful physics-based simulations.
Take the example of a system capturing camera images to train an ADAS algorithm. An algorithm is only as good as its training data, which must be as real as possible. That means capturing thousands of kilometres of driving data—though driving thousands of kilometres will not always yield critical corner cases.
Ansys and Synopsys have toolchains that can simulate those sensors. For instance, simulating a rainy environment to see how rain affects light deflection and capturing images as close to reality as possible. Because physics is the closest thing to reality, you can generate rich data, model your environment to surface rare corner cases, and test your algorithms against them.
We also combine physics-based simulation with digital twin technology. AI works hand-in-hand with trusted physics-based simulations rather than operating as a standalone technology.
ELE Times: How do you ensure vehicular safety, real-time control, and high uptime in harsh weather environments like temperature fluctuations, fog, and rain?
MM: Safety must be designed into the mindset right from day one. In critical driving situations like sudden obstacles, decisions happen in milliseconds, making timing vital. Think of an aircraft pilot flying where the speed gauge fails—you cannot pull over to the side or land anywhere. Safety cannot be an afterthought; it must be incorporated while building the system.
This is why standards like DO-178C for aerospace and ISO 26262 for automotive exist. When systems are built following these standards, sensors have built-in redundancies, and systems are designed to operate during both expected and unexpected situations.
While you can run a car through physical fog and rain, dense fog and specific weather conditions are not always available on demand. Furthermore, physical prototype testing takes time. By utilising “shift left” methodologies and physics-based simulations, we test data on a PC much earlier in the cycle to evaluate vehicle behaviour before building physical prototypes.
ELE Times: How do you deal with adversarial machine learning to ensure it doesn’t interfere during the development process?
MM: I look at it across three primary areas:
- Sensor Redundancy: Ensuring multiple sensors capture data so that if one fails, backup sensors continue functioning correctly.
- Extensive Testing: Conducting comprehensive testing across both expected and unexpected scenarios to refine and tweak software algorithms against edge cases that might otherwise fail.
- Virtual Integration: Bringing modules together virtually on a PC to test interactions, run scenarios, and evaluate performance using virtual ECUs and physics-based simulations.
ELE Times: Vehicle manufacturers are rapidly introducing new features and technicalities. How much of a challenge is this when balancing feature rollouts with strict safety norms?
MM: People often view development speed and safety as competing objectives, but that mindset needs to change. Safety-critical applications like braking, steering, powertrain control, and ADAS require the highest level of verification—what we call ASIL D—which demands time and care.
However, certain non-critical features can follow agile development processes. Nothing is more important than the safety of the people inside and outside the vehicle. New features are great, but never at the cost of safety.
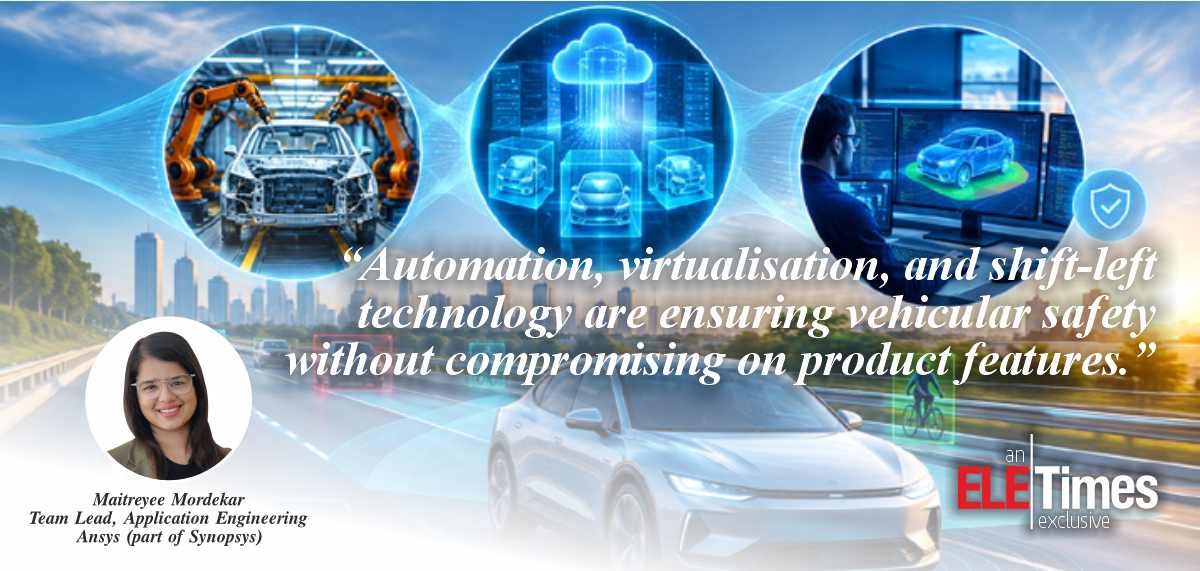
This balance is achieved through automation, virtualisation, and shift-left technology. By validating early and reducing reliance on physical hardware waiting times, speed and safety stop competing and instead find a healthy balance where safety is never compromised for features.
ELE Times: How do you view the Indian market in terms of safety-critical equipment and safety regulations compared to the global automotive market?
MM: While autonomous vehicles are being developed globally, features deployed in North America or Europe cannot always be directly translated to the Indian context. Driving conditions, road infrastructure, passenger behaviour, and pedestrian patterns are completely different in India.
Consequently, OEMs roll out solutions more carefully in India due to complex traffic environments and a unique mix of vehicles and driving behaviours. Virtual validation plays a major role here by allowing manufacturers to run millions of driving scenarios virtually before deployment, accelerating validation for Indian conditions and making the local market safer.
ELE Times: How critical is cybersecurity in connected cars and modern vehicles, and what measures ensure passenger data and vehicle software remain secure from misuse?
MM: October is Cybersecurity Month, so it is fitting to discuss this. In general contexts, cybersecurity is about data protection. But in a vehicle context, a hacker breaking into a car is rarely just after data—they are more likely looking to harm people inside or outside the vehicle.
The primary concern is minimising vulnerabilities in software design that could lead to threats. Through Threat Analysis and Risk Assessment (TARA), engineering teams identify threat conditions and scenarios, build attack trees, and implement mitigation strategies like redundancies to keep passengers safe.
Toolchains like Ansys Medini support cybersecurity analysis. Alongside secure design from day one, systems must undergo extensive testing against various test cases using physics-based simulations, virtual validation, and software testing to evaluate the system as a whole.
ELE Times: Looking ahead, what can we expect from Ansys and Synopsys in automotive technology development looking toward 2027?
MM: The very first thing you will notice is how Ansys and Synopsys coming together makes silicon-to-systems workflows much more amalgamated. This will enable our customers to develop and build complete mobility systems right on their PCs even before those technologies physically make their way into a vehicle.

